Everything here runs in my home lab. Each project links to a write-up explaining what I built and why, plus the code on GitHub.
Threat intel dashboard (Splunk + AlienVault OTX)
I built a Splunk dashboard that correlates AlienVault OTX threat intel against live Sysmon endpoint telemetry. Malicious IPs, domains, and hashes from OTX get matched against real activity on my Windows hosts. I built it for the ECA Cyber Range Splunk Security Dashboard Challenge.
Tools: Splunk, Sysmon, AlienVault OTX
Linux STIG compliance monitoring (OpenSCAP + Splunk)
I hardened an Ubuntu 24.04 VM and raised STIG compliance from 50.48% to 78.39%. An eight-panel Splunk dashboard maps the findings to ATT&CK techniques.
Tools: OpenSCAP, Splunk, Ubuntu
ATT&CK: T1110, T1548.003, T1562.006, T1078, T1046, T1543, T1070
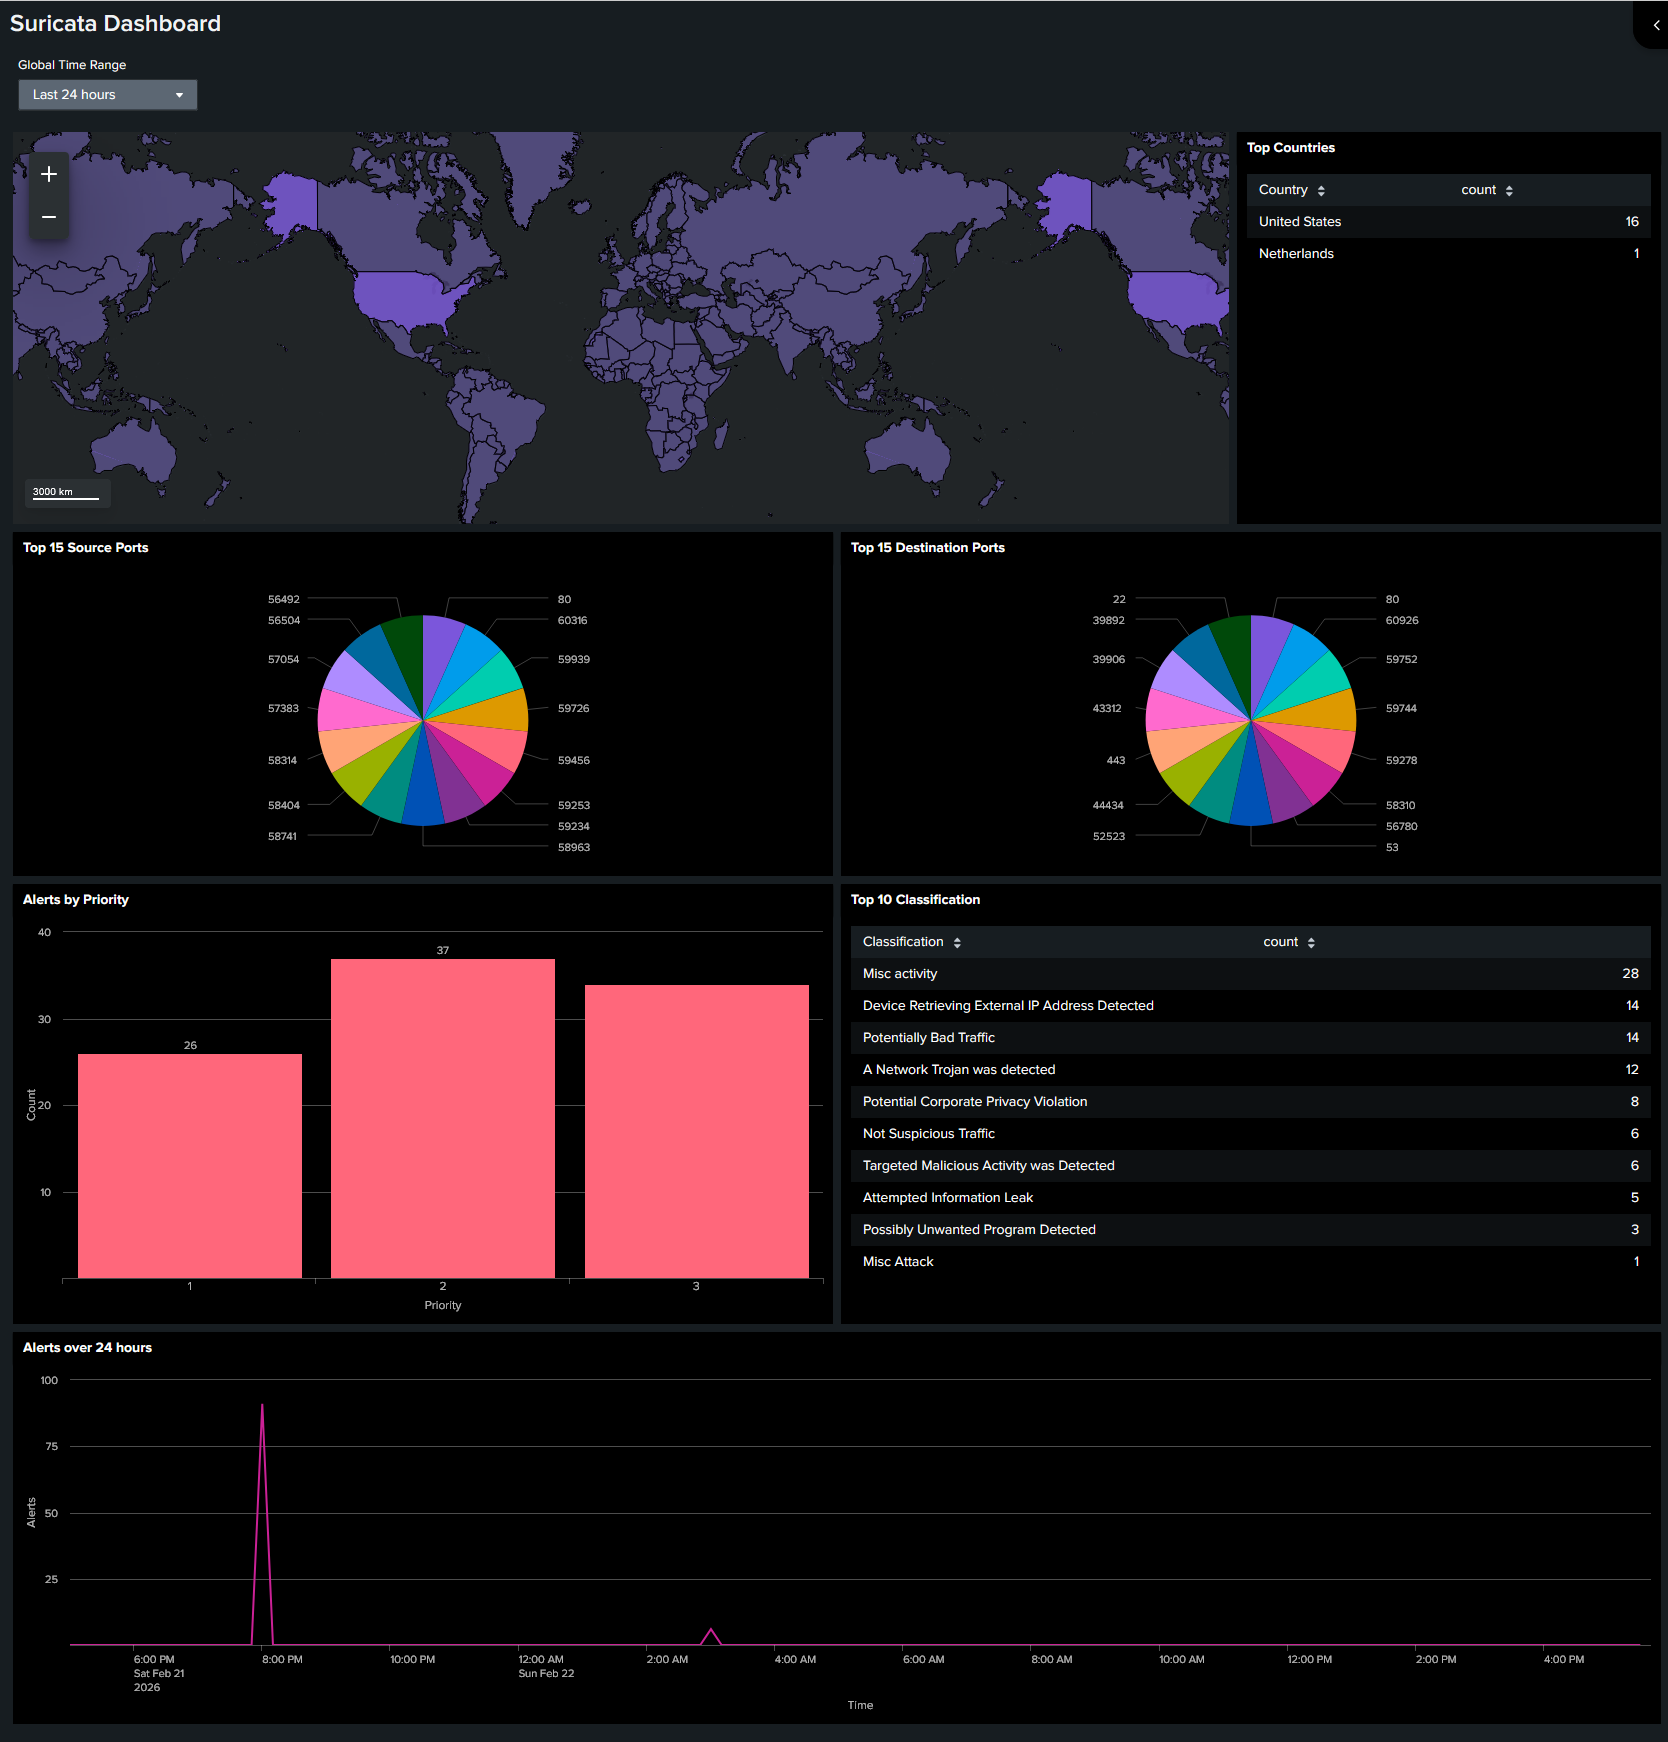
Network IDS on a Raspberry Pi 4
I run Suricata on a Pi 4 behind a port-mirrored switch and forward alerts to Splunk. My goal was to see what the devices on my network were doing, not to watch every site my family visits. Then I tuned out the Emerging Threats noise.
Tools: Suricata, Splunk, Raspberry Pi
The Simple series: Python triage tools
Small CLI tools that each solve one triage problem. The phishing analyzer parses SPF, DKIM, and DMARC and checks attachments against VirusTotal and MalwareBazaar. The IOC enricher pulls from AbuseIPDB, VirusTotal, and WHOIS.
Tools: Python, VirusTotal, MalwareBazaar, AbuseIPDB
ATT&CK: T1566 and others
Windows 11 STIG remediation scripts
I write PowerShell scripts that fix DISA Windows 11 STIG v2r8 findings across account policy, audit policy, user rights, and system hardening. I validate every fix with a Tenable Nessus compliance scan.
Tools: PowerShell, Tenable Nessus
Sigma detection rules
My portable library of Sigma rules. I convert them to Splunk SPL with sigma-cli so the same detection logic can move between SIEMs.
Tools: Sigma, sigma-cli, Splunk
In progress
NIST CSF 2.0 gap analyzer. A Python tool that compares an organization’s self-assessed controls against CSF 2.0 and generates a gap report.